> ## Documentation Index
> Fetch the complete documentation index at: https://docs.superblocks.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Code Security
> Superblocks-managed policies that check the code and dependencies in your apps at install, publish, and in production
export const Alert = ({type, title, children}) => {
const variant = ["info", "success", "warning", "danger", "note"].includes(type) ? type : "note";
return
{title &&
{title}
}
{children}
;
};
**Code Security** is a set of Superblocks-managed policies that check the code and dependencies shipping in your applications. They let builders move fast on AI-generated code without leaving the Superblocks editor. Superblocks writes and maintains these policies, so there is nothing to author. What separates them from each other is **when they run** and **what they look for**.
## When each policy runs
The **Policy Agents** page in the dashboard lists every Superblocks-managed policy, grouped by when it runs.
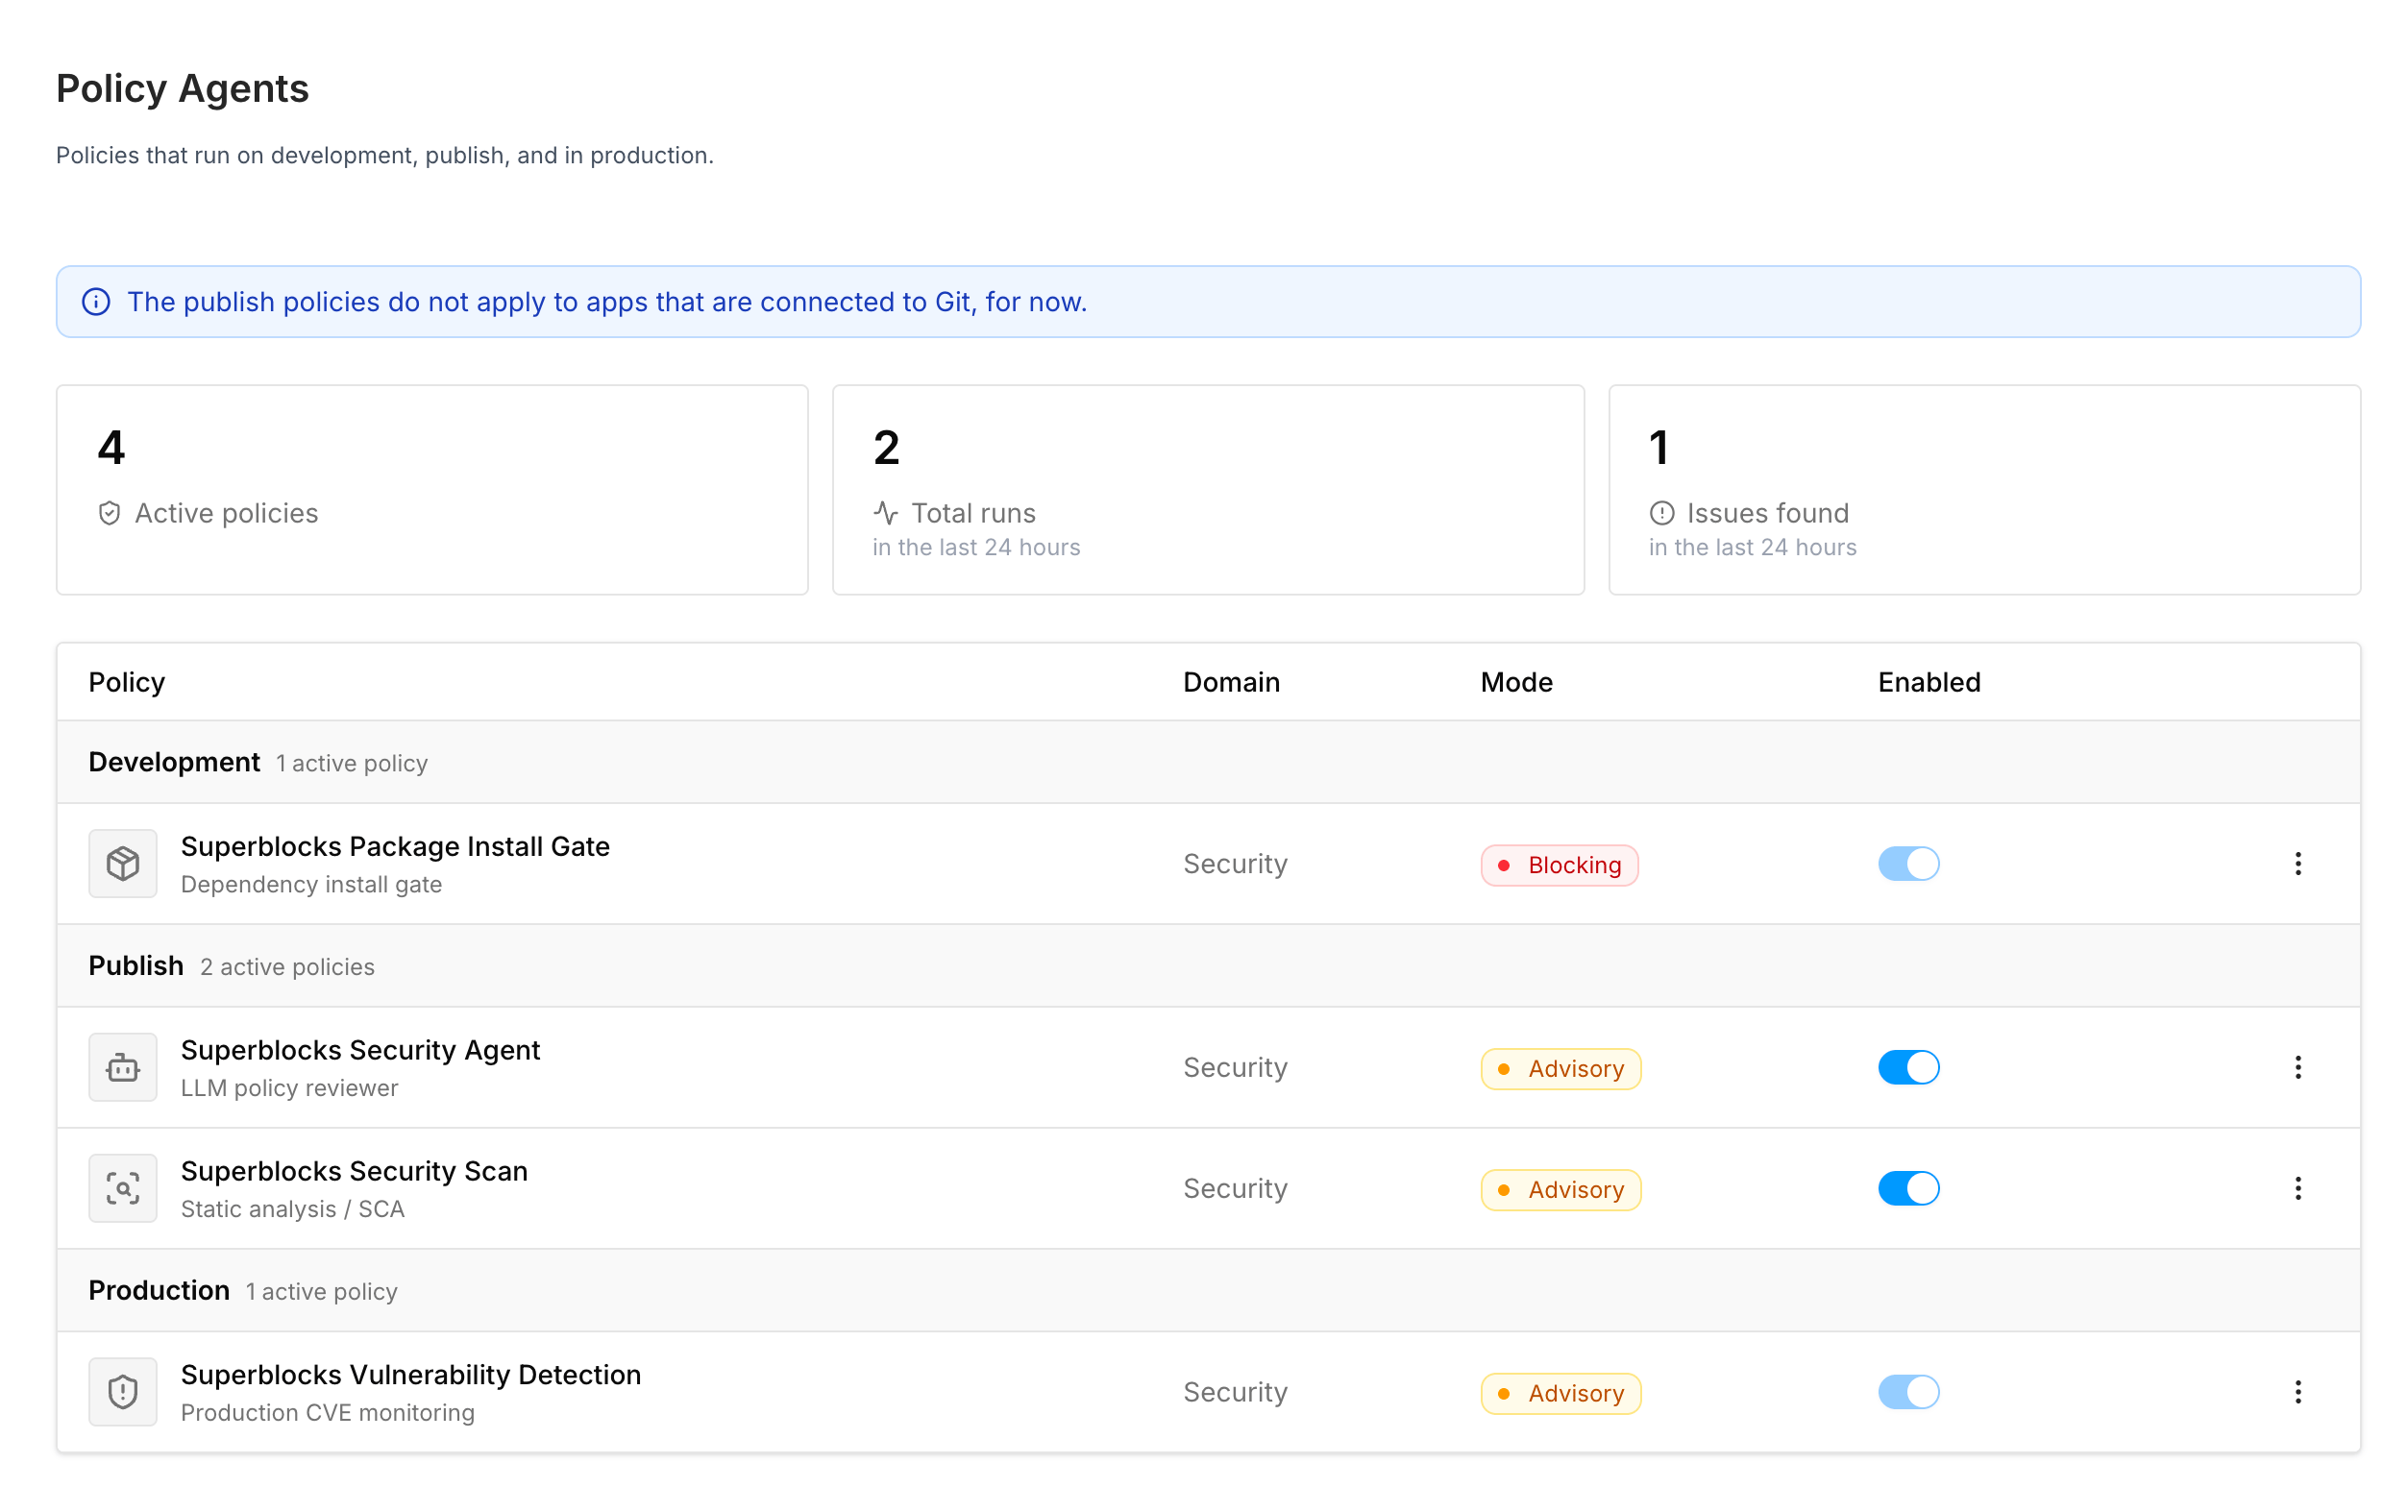 | Moment | Dashboard name | What it does | Where the result appears |
| --------------- | ----------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Development** | Superblocks Package Install Gate | [CVE detection](/admin/code-security/supply-chain/cve-detection) before Clark adds a package, including malware advisories and a 7-day cooldown on brand-new npm releases | Clark chat, when the package is requested |
| **Publish** | Superblocks Security Scan | [Static analysis](/admin/code-security/static-analysis) of source and built artifacts, plus [CVE detection](/admin/code-security/supply-chain/cve-detection) on the snapshot being published | **Pre-Publish Policies** on the publish detail |
| **Publish** | Superblocks Security Agent | The [Security Agent](/admin/code-security/security-agent) reviews the application the way a security engineer would | **Pre-Publish Policies** on the publish detail |
| **Production** | Superblocks Vulnerability Detection | [CVE detection](/admin/code-security/supply-chain/cve-detection) re-runs against published apps as new advisories appear | [Security Center](/admin/code-security/supply-chain/cve-detection#continuous-monitoring) and [notifications](/admin/code-security/supply-chain/cve-notifications) |
Pre-publish policy agents are currently skipped for apps [connected to Git](/development-lifecycle/version-control/connect-to-git). For Git-connected apps, run equivalent security checks in your CI pipeline. The Policy Agents page shows this limit.
CVE detection is one policy evaluated at three moments. At development time it is the Package Install Gate in Clark chat, with malware checks and the cooldown on top of the CVE lookup. At publish time it is part of the Security Scan. In production it is Vulnerability Detection, against apps already live.
## What each policy looks for
Deterministic scanning for hardcoded secrets and insecure code patterns
An AI reviewer that reasons about your application the way a security engineer would
Known advisories against the npm packages your app depends on
Static analysis and the Security Agent are complementary. Static analysis matches known-bad patterns and is deterministic, so the same code always produces the same findings. The Security Agent reasons about application logic and catches issues pattern matching misses, such as a missing authorization check or PII returned in an API response.
## Shared behavior
Once a publish-time policy produces a finding, the rest is the same no matter which policy found it: severity, scan mode, remediation with **Fix with Clark**, run errors, and the audit trail. That is covered once in [How findings work](/admin/code-security/how-findings-work).
The short version: **only** **critical** and **high** findings can block a publish, and whether they do depends on the [scan mode](/admin/code-security/how-findings-work#scan-modes) an admin sets per policy.
CVE detection applies whether you use the default public registry or configure an optional [private registry](/admin/code-security/supply-chain/private-registries).
## Packages
Beyond the policies themselves, Superblocks gives you visibility and control over the packages your apps depend on:
* **[CVE notifications](/admin/code-security/supply-chain/cve-notifications)**: alert admins and app creators when a newly disclosed critical or high CVE lands on a published app
* **[CVE exceptions](/admin/code-security/supply-chain/cve-exceptions)**: template packages Superblocks excludes because the advisory is not exploitable and cannot be upgraded today
* **[SBOM](/admin/code-security/supply-chain/sbom)**: view and export an application's package inventory as a CycloneDX document
* **[Private registries](/admin/code-security/supply-chain/private-registries)**: route every `npm install` through a registry your security team already trusts, such as CodeArtifact, Artifactory, or Nexus
## Permissions
**`policies:manage`** configures policies, modes, and scope. **`policies:view`** reads policies and sees every application in Security Center. Without `policies:view`, a builder still opens Security Center for the applications they can edit. Deploy access gates **Fix with Clark**, **Unpublish**, and **Publish anyway**.
## Related
* [How findings work](/admin/code-security/how-findings-work): severity, scan modes, remediation, and audit
* [Knowledge](/building-with-clark/knowledge/index): guide Clark while it writes code, so fewer findings appear at publish time